Listen to this podcast for free in the app: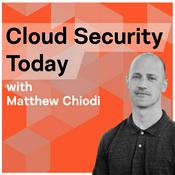 Download for free in the App Store
radio.net
Sleep timer
Save favourites
63 episodes
The psychology of CISO
2026/10/06 | 54 mins.CISOs are accountable for cyber risk—but do they have the authority to change it?
In this episode of Cloud Security Today, Matt sits down with cybersecurity researcher Raghav Singh to explore how organizational culture, power dynamics, and emerging AI capabilities shape security outcomes. Drawing on a burnout study involving 37 CISOs, Raghav explains how resource constraints and communication challenges reinforce one another—and why experience doesn’t necessarily make the job less stressful.
They discuss why reporting to the CEO doesn’t guarantee influence, how AI could replace alert fatigue with the burden of explaining machine-generated judgments, and emerging research into how attacks take shape before execution.
The conversation closes with three practical actions: align accountability with authority, address recurring organizational friction, and examine incidents as connected sequences of behavior rather than isolated alerts.The AI harness
2026/08/20 | 51 mins.AI security has a hype problem.
Every week brings a new headline about agents escaping sandboxes, AI replacing security teams, or models becoming “too smart” to control. But the more useful question for CISOs is much more practical: where do the actual security controls belong?
In this episode, I sit down with Diana Kelley, CISO at Noma Security and one of the clearest voices in AI security, to separate AI mythology from operational reality.
Diana explains why the LLM itself is not the security boundary, why the “harness” around the model matters, and how security teams should think about contamination, consequence, and runtime control as agentic AI moves into the enterprise.
This conversation is not about AI hype. It is about what CISOs, security architects, and technical leaders need to understand before AI systems start taking autonomous action at machine speed.
What You’ll Learn
Why AI security is different from traditional AppSec
What an AI “harness” is and why it matters
Why the LLM should not be treated as a security control
How prompt injection relates to trust boundaries and context windows
Why agentic AI increases both speed and consequence
Key Takeaways
The model is not the control point.
The LLM is powerful, but it is not deterministic enough to serve as the primary security boundary. Security controls need to live before and after inference — in the harness, surrounding software, workflow, and runtime environment.
Think in terms of contamination and consequence.
Contamination is what enters the context window. Consequence is what the system does after inference. Both need controls, especially when AI agents can act repeatedly and autonomously.
Agentic AI changes the scale problem.
A single bad prompt is one thing. Hundreds or thousands of agents looping through tasks at machine speed is another. The risk is not just bad output. It is autonomous action without adequate guardrails.Cyber and the NY Giants
2026/07/01 | 47 mins.Christina Morillo shares her unconventional career journey from traditional IT to cybersecurity in the NFL, highlighting the importance of building trust, understanding business risk, and addressing misconceptions in cybersecurity.
Christina's book: Zero Trust NetworksIdentity for AI agents
2026/05/10 | 45 mins.AI agents are moving from answering questions to taking action. That changes everything for identity and access management.
In this episode, Ken Huang joins Matt to break down why traditional IAM was not built for agentic AI, where service accounts and OAuth scopes fall short, and what CISOs should do now to govern agents before they hit production at scale.
Episode Links
Ken's substack
Ken's paper from 2011 on AI (he was way ahead!)
NIST AI RMFThe future of CISO
2026/04/11 | 44 mins.In this episode, Michael Piacente shares insights on career transitions in IT and security, the evolving role of CISOs, and the impact of AI on security talent and practices. Discover how community, storytelling, and strategic hiring shape the future of cybersecurity leadership.
Resources
The 2026 Global CISO Leadership Report
Hitch Partners
NIST AI Framework
More Business podcasts
Trending Business podcasts
About Cloud Security Today
The Cloud Security Today podcast features expert commentary and personal stories on the “how” side of cybersecurity. This is not a news program but rather a podcast that focuses on cyber leadership and understanding the threats most impacting organizations today.
Podcast websiteListen to Cloud Security Today, The Money Show and many other podcasts from around the world with the radio.net app
Get the free radio.net app
- Stations and podcasts to bookmark
- Stream via Wi-Fi or Bluetooth
- Supports Carplay & Android Auto
- Many other app features
Get the free radio.net app
- Stations and podcasts to bookmark
- Stream via Wi-Fi or Bluetooth
- Supports Carplay & Android Auto
- Many other app features
Cloud Security Today
Scan code,
download the app,
start listening.
download the app,
start listening.
 South Africa